AWS SCPs for a Landing Zone: Guardrails Before You Migrate
The deny-based Service Control Policies to attach before you migrate workloads into an AWS landing zone, with the config, the deny-list trade-off, and what to check first.
Blog
Notes from real engagements: landing zones, pipelines, on-call, and the security work that gets left until an audit. No thought leadership, no funnels.
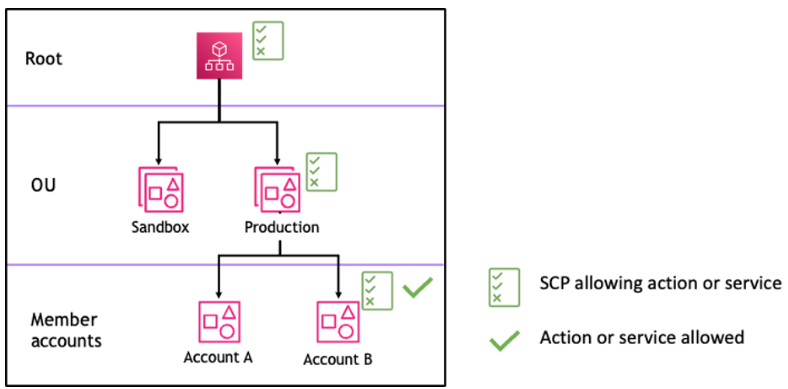
The deny-based Service Control Policies to attach before you migrate workloads into an AWS landing zone, with the config, the deny-list trade-off, and what to check first.
How to stand up a VPC Service Controls perimeter in dry-run mode, read the violations, and only then enforce it, so migrating sensitive data into Google Cloud does not lock out your own pipelines.
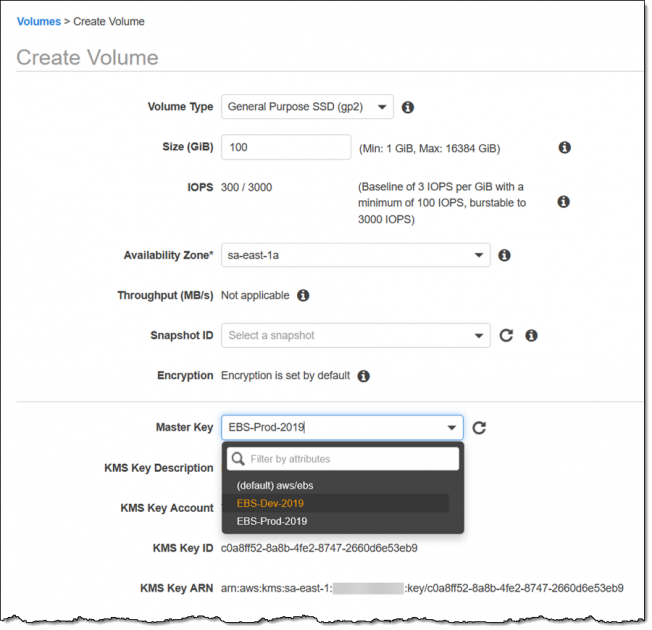
You cannot flip an unencrypted EBS volume to encrypted in place. Here is the snapshot-and-swap workflow, how to enforce encryption by default per Region, and the KMS traps that bite after a migration.
The assistant will scope your problem in a couple of minutes.